How Post-Purchase Service Providers Use Tracking Data to Serve Multiple Brands with One API
Post-purchase service providers can serve multiple brands through one tracking API integration by collecting shipment updates centrally, matching each shipment to the right brand and order, and delivering a brand-specific experience through each client’s own channels. The shared connection simplifies tracking-data collection; it does not remove the need for separate customer data, messaging rules, permissions, and service workflows for every brand.
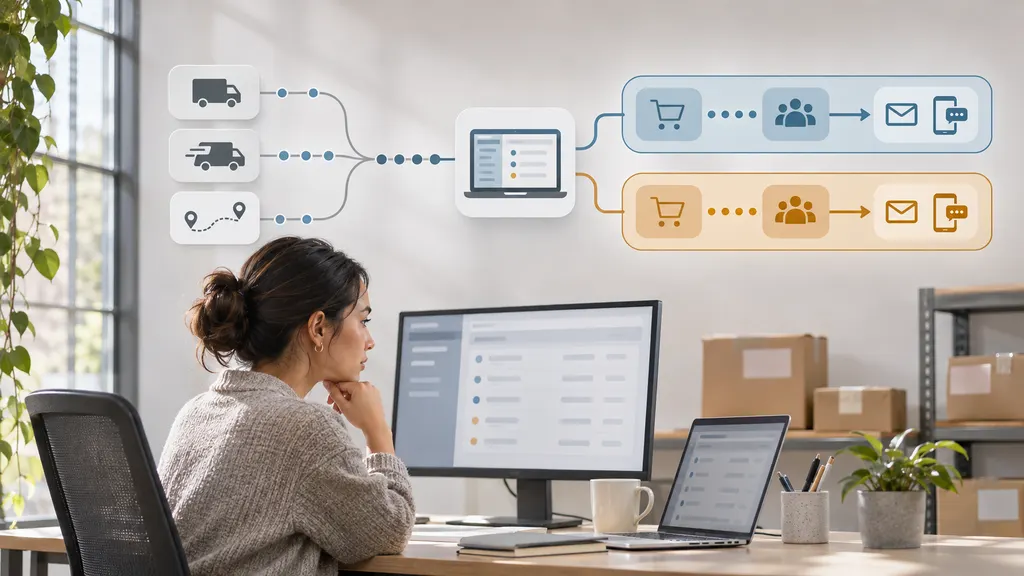
This model is useful for agencies, customer-support platforms, fulfillment partners, and other providers that manage delivery communications on behalf of several merchants. The practical question is not simply whether one API can return a tracking status. It is whether the provider can turn that status into a reliable, appropriately branded action without showing one client’s data to another.
What the shared API actually does
A tracking API gives the service provider a programmatic way to submit or look up shipment identifiers and receive tracking information. Instead of building a separate carrier-facing integration for every merchant, the provider can make tracking data available to its own application through a common upstream connection. The provider’s application then decides which brand owns the shipment and what to do with the information.
That distinction matters. One tracking API is not the same thing as one shared customer account, one tracking page, or one notification template. The upstream integration addresses data collection. The service provider remains responsible for its downstream product: merchant onboarding, order matching, customer-facing language, access controls, support tools, and records of what was communicated.
A workable architecture has three layers. First, an ingestion layer accepts a shipment reference and obtains tracking updates. Second, an internal shipment record links those updates to the correct merchant, order, carrier, and recipient. Third, a presentation layer uses the merchant’s rules to decide whether to update an order page, alert a support agent, or send a customer message. Keeping these layers separate makes it easier to add another brand without rewriting the tracking connection.
Follow one shipment from registration to customer action
Consider a provider managing delivery updates for two unrelated online stores. Both stores send shipment details to the provider, but each record must include a tenant identifier: the provider’s unambiguous internal key for the brand that owns it. The provider also needs enough information to match the shipment to an order. A tracking number alone may not be a safe global key, because shipments can involve different carriers, reused identifiers, or corrections to the original order data.
- Register the shipment. Receive the brand identifier, order reference, tracking number, and any other permitted details needed for matching. Validate the input before requesting tracking data. Store credentials and customer contact information separately from general tracking-event records where practical.
- Collect and retain the source update. Retrieve tracking information through the upstream API using its documented methods. Preserve the source status, event description, timestamp, and location when supplied. Avoid replacing the original event with only a simplified label; support teams may need the underlying wording to investigate an exception.
- Normalize carefully. Map source events into a small internal set of states, such as in transit, out for delivery, delivered, or exception. Keep the original event alongside that mapping. A broad state is useful for automation, but it can hide distinctions that matter to a customer or support agent.
- Apply brand rules. One merchant may want an out-for-delivery email; another may only want an order-page update. Decide eligibility using the brand’s configuration, the customer’s communication preferences, the event’s freshness, and the history of messages already sent.
- Record the outcome. Save which event triggered which action, which brand policy was applied, and whether delivery to the downstream channel succeeded. This provides a trail for troubleshooting duplicate notifications and customer complaints.
The same upstream status may therefore produce different actions for different brands. That is the point of the shared-service model: centralize collection and operational maintenance while preserving each merchant’s customer relationship.
The design decisions that determine whether it scales
Make tenant ownership explicit
Every shipment, event, order mapping, notification rule, and customer-facing link should resolve to a specific tenant. Check tenant ownership when data enters the system and again when an application or support user reads it. A merchant-branded page should not rely on a tracking number alone to determine which customer record to display. Access should be constrained by the authenticated merchant or by a suitably scoped customer link.
Separate credentials and permissions according to the actual account model offered by the upstream provider and the contractual relationship with each merchant. A single technical integration does not automatically grant permission to pool all merchant data or give every client the same visibility. Document who may register shipments, retrieve events, export records, and change notification settings.
Treat tracking events as updates, not guaranteed commands
Tracking information can arrive after a delay, appear out of order, or contain a correction. A system that sends a new message every time it reads an event risks duplicate or misleading emails. Use a stable event key when the source supplies one; otherwise define a documented deduplication rule using available shipment and event fields. Store when the provider observed an update separately from the event time reported by the source.
Do not assume that every shipment follows the same sequence of states. An exception might later be resolved, and an event with a later arrival time may describe an earlier physical scan. Before using a status to trigger a promise or escalation, decide how the application handles stale, conflicting, or missing information. For a customer-facing claim such as delivery, show the supporting event rather than implying that an internal label proves more than the source record says.
Plan for polling, callbacks, and failures
The provider’s update strategy must follow the upstream API’s actual documentation. If callbacks are available for the relevant account and event type, the application still needs to authenticate incoming requests, handle retries, and process duplicate deliveries safely. If it polls, it needs a schedule that respects documented limits and avoids unnecessary repeated requests. Neither approach eliminates the need for recovery when an update is missed or a downstream notification fails.
HTTP responses also need to be interpreted correctly. An accepted request, for example, should not be treated as proof that a shipment has already received a new tracking event. The HTTP Semantics specification defines response-code meanings; the tracking provider’s own documentation must establish what a particular API response means for shipment registration or retrieval. Build monitoring around both technical failures and business failures, such as a valid response that cannot be matched to an order.
What to verify before choosing a tracking API
For a multi-brand provider, the best integration is the one that fits the entire operating model, not merely the one that returns a sample tracking result. Ask prospective providers to show how their documented API supports the shipments and workflows you actually handle. A short proof of concept should include multiple merchants, the carriers those merchants use, and at least one incomplete or problematic shipment record.
- Shipment intake: What identifiers and carrier details are required? How are invalid or duplicate submissions reported? Can the application associate its own order or tenant reference with a request, or must that association remain entirely in its database?
- Update delivery: Are updates retrieved, pushed, or both for the relevant plan? What are the documented request limits, retry expectations, authentication methods, and error responses? Verify these against the current documentation rather than assuming that a feature described at a high level is available in every configuration.
- Event quality: Which original fields are returned, and how should timestamps, carrier names, locations, and delivery-related events be interpreted? Test with real shipment examples for the merchants being onboarded.
- Tenant operations: Can the provider separate access, usage accounting, and support investigations by client within its own system? If it needs upstream account separation, confirm whether and how that is supported before committing to the architecture.
- Data handling: What customer or shipment information must be sent upstream? Review retention, deletion, security, and contractual requirements with the parties responsible for that data. API security guidance, including the OWASP API Security Project, provides a useful basis for examining authorization and access risks.
17TRACK’s Tracking API page and developer documentation are relevant starting points for a provider evaluating a shared tracking integration. Treat the documentation as the authority for implementation details, and confirm the required methods, supported shipment scenarios, access terms, and commercial arrangements for the intended use before building a multi-client service around them. A public API page by itself does not establish that every desired merchant workflow is supported.
Where the provider should keep control
Tracking data can inform a post-purchase experience, but it should not dictate the entire experience. The provider should own the mapping from shipment to merchant, the rules for customer contact, and the language used when an update is uncertain. If an event says only that a parcel reached a facility, the branded message should not promise a delivery date. If tracking stops updating, the system should distinguish a lack of new information from proof that the parcel is lost.
Support workflows deserve equal attention. Give authorized agents the original tracking event, the normalized status, the time each was recorded, and the notification history. That view helps an agent explain why a customer saw a particular message and decide whether an issue needs further investigation. It also makes a multi-brand operation easier to audit: a problem can be traced to an upstream update, a matching error, a merchant rule, or a messaging failure instead of being blamed vaguely on the API.
Start with a narrow pilot. Connect one or two merchants, register representative shipments, and test ordinary delivery events alongside exceptions, missing carrier details, duplicate updates, and corrected orders. Confirm that each brand sees only its own shipments and that a failed notification can be retried without creating a second customer message. Add more merchants only after those behaviors are predictable. One API can reduce integration work, but dependable service across brands comes from the controls built around it.
FAQ
Does one tracking API mean every brand uses the same tracking page?
No. The API can supply tracking information to the provider’s application, while each brand keeps its own page design, domain arrangements, customer language, and notification rules. Those branded experiences must be implemented and maintained separately.
Can a tracking number identify the right brand by itself?
It should not be the sole tenant identifier. Save an explicit brand or tenant key when the shipment enters the system, then associate the tracking number with that brand’s order record. Check the association again before displaying shipment information or sending a message.
Should a provider send a notification for every new tracking event?
Usually not. Some events are repetitive, delayed, or too technical to help a customer. Define which event types qualify, suppress duplicates, check communication preferences, and retain the original update for support review.
What should be tested before adding another merchant?
Test the merchant’s actual shipment inputs, carrier mix, order matching, access permissions, notification rules, and exception handling. Include a case where tracking data is missing or late, and verify that no shipment or customer information can cross into another merchant’s account.